Build and Maintain a Secure, CMMC-Ready Environment 

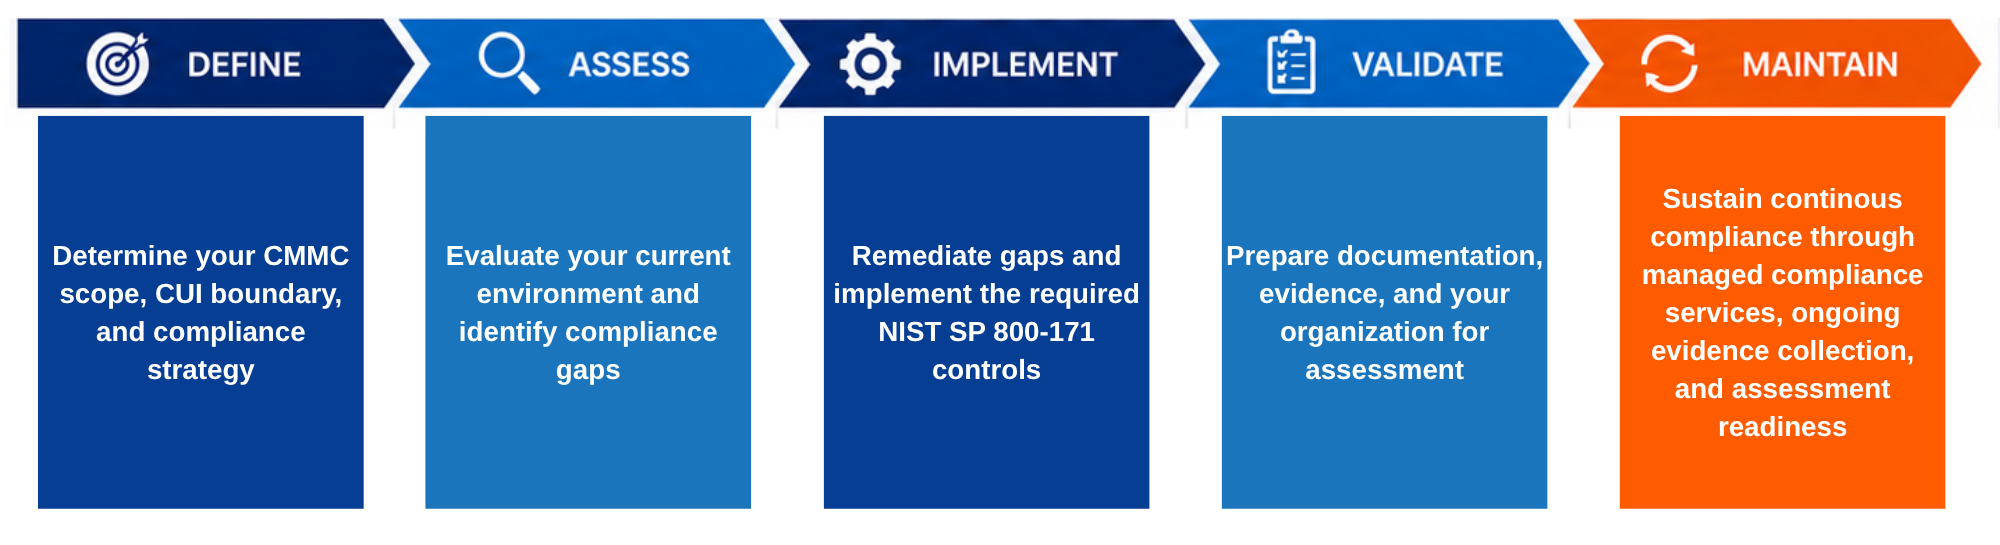
CorpInfoTech helps defense contractors build and follow a practical roadmap for CMMC/NIST 800-171 compliance through secure IT operations, managed compliance, remediation, monitoring, and ongoing support, helping you protect CUI, maintain a secure environment, and build continuous compliance into your day-to-day operations.
CMMC Roadmap 2000x1200 (1)

Why a Certified CMMC Matters for CMMC

If your managed service provider supports systems within your CMMC boundary, their security practices can directly impact your assessment readiness, their security practices can directly affect your CMMC compliance, evidence, and assessment readiness. 

As a CMMC Level 2 Certified MSP, Cyber AB Registered Provider Organization (RPO), and CIS Controls Accredited organization, CorpInfoTech helps defense contractors strengthen cybersecurity, protect CUI, and support CMMC compliance through proven practices and operational experience. 

Through our Technology Assurance Services (TAS) for CMMC Compliance, we help organizations align cybersecurity, compliance, documentation, and ongoing operations into a structured program that supports assessment readiness and continuous compliance.

If you need support with CMMC Level 1 requirements, explore our tailored solutions - explore our CMMC Level 1 solutions


Not sure where your organization stands? CorpInfoTech can help you understand your scope, identify remaining gaps, and determine the practical next steps toward maintaining CMMC/NIST 800-171 compliance. 

The CorpInfoTech Advantage

From CMMC Roadmap to Continuous Compliance

The path to CMMC/NIST 800-171 compliance does not end with implementing controls or preparing for an assessment. Organizations need to maintain a secure environment, keep documentation and evidence current, monitor changes, and ensure controls continue to operate as intended. 

CorpInfoTech brings cybersecurity, compliance, and managed IT together to help defense contractors move through their compliance roadmap and establish continuous compliance as part of ongoing operations


Turn Your CMMC Roadmap into an Ongoing Compliance Program 

 Achieving CMMC/NIST 800-171 compliance is only part of the journey. Maintaining it requires ongoing attention to your security environment, documentation, evidence, controls, and changing business and technology needs.

TAS for CMMC brings together managed IT, cybersecurity, and compliance support to help defense contractors put their compliance roadmap into practice and maintain it over time.  

With CorpInfoTech, your organization can:

  • Maintain a secure CUI environment through managed IT and cybersecurity practices aligned with your compliance requirements.
  • Address compliance gaps with coordinated remediation and implementation support.
  • Keep documentation and evidence current as systems, users, processes, and requirements change.
  • Monitor and validate controls to help ensure they continue to operate as intended.
  • Support continuous compliance by integrating security and compliance activities into ongoing IT operations.

The result is a more sustainable approach to CMMC/NIST 800-171—one designed to help your organization protect CUI, demonstrate compliance, and maintain readiness over time. 

Access Additional Information Through our Blogs

Is CMMC Going Away? Here's What Defense Contractors Need to Know
By Waits Sharpe 24 August 2026

On July 13, 2026, the Department of War (DoW) announced an immediate 60-day pause of CMMC Phase 2...

Read More
CMMC Phase 2 Is Paused. Here's Why Defense Contractors Should Stay the Course
By Waits Sharpe 22 July 2026

On July 13, 2026, the U.S. Department of War released a statement announcing the "immediate...

Read More